01
Penetration testing & red teaming
Human-led attacks on your web apps, APIs, mobile and internal networks. We chain low-severity bugs into the breach a real adversary would pull off.
- Web & API
- Red team ops
- Social engineering
Launching soonREVENGE opens to its first clients soon. Read the announcement
REVENGE attacks your web apps, APIs, cloud and AI systems the way real adversaries do, then hands your engineers the fix. Every finding comes with a working exploit, and the hardening scales with everything you ship.
Supported by the startup programs of

# REVENGE: Strike first.

> REVENGE is an offensive security company. We attack web apps, APIs, cloud infrastructure and AI/LLM systems the way real adversaries do, validate every finding with a working exploit, and deliver the fix as code. We also run a 24/7 incident response team with a 15-minute response SLA.

REVENGE attacks your web apps, APIs, cloud and AI systems the way real adversaries do, then hands your engineers the fix. Every finding comes with a working exploit, and the hardening scales with everything you ship.

- Website: https://revengeaisecurity.com/
- Contact: contact@revengeaisecurity.com
- Request a demo: https://revengeaisecurity.com/#top-form
- Incident response (24/7/365, 15-minute SLA): contact@revengeaisecurity.com
- Languages: [English](https://revengeaisecurity.com/index.md), [Français](https://revengeaisecurity.com/fr/index.md)
- Tested against and mapped to these frameworks: ISO 27001, SOC 2, PCI DSS 4.0, NIS2, DORA, GDPR, HIPAA, OWASP Top 10, OWASP LLM Top 10, MITRE ATT&CK, CIS Benchmarks, EU AI Act
Tested against and mapped to these frameworks
 ISO 27001
 SOC 2
 PCI DSS 4.0
 NIS2
 DORA
 GDPR
 HIPAA
 OWASP Top 10OWASP LLM Top 10
 MITRE ATT&CK
 CIS BenchmarksEU AI Act
What we do
We cover everything from the first line of code to planet-scale production, including the AI agents now running inside it. One team of operators handles all six disciplines, so nothing gets handed off.
Human-led attacks on your web apps, APIs, mobile and internal networks. We chain low-severity bugs into the breach a real adversary would pull off.
We red team your models and agents for prompt injection, jailbreaks, tool abuse and data exfiltration, tested against the OWASP LLM Top 10.
Secure code review, threat modeling and DAST run inside your pipeline, so vulnerabilities get caught in the pull request before they reach production.
We attack AWS, GCP, Azure and Kubernetes from the inside. We map your IAM blast radius, kill toxic misconfigurations and lock down your crown jewels.
24/7 managed detection with a 15-minute incident response SLA. When the alarm goes off, our operators are already in the room.
We get you ready for ISO 27001, SOC 2, PCI DSS, NIS2 and DORA with evidence auditors accept, which helps you close enterprise deals.
## Hardening for everything you ship.

We cover everything from the first line of code to planet-scale production, including the AI agents now running inside it. One team of operators handles all six disciplines, so nothing gets handed off.

### Penetration testing & red teaming

Human-led attacks on your web apps, APIs, mobile and internal networks. We chain low-severity bugs into the breach a real adversary would pull off.

Keywords: Web & API, Red team ops, Social engineering

### AI & LLM security

We red team your models and agents for prompt injection, jailbreaks, tool abuse and data exfiltration, tested against the OWASP LLM Top 10.

Keywords: Prompt injection, Agent abuse, Model theft

### Application security

Secure code review, threat modeling and DAST run inside your pipeline, so vulnerabilities get caught in the pull request before they reach production.

Keywords: Code review, Threat modeling, DAST in CI

### Cloud & Kubernetes hardening

We attack AWS, GCP, Azure and Kubernetes from the inside. We map your IAM blast radius, kill toxic misconfigurations and lock down your crown jewels.

Keywords: IAM paths, K8s, CSPM

### Detection & incident response

24/7 managed detection with a 15-minute incident response SLA. When the alarm goes off, our operators are already in the room.

Keywords: 24/7 MDR, Forensics, Ransomware

### Compliance acceleration

We get you ready for ISO 27001, SOC 2, PCI DSS, NIS2 and DORA with evidence auditors accept, which helps you close enterprise deals.

Keywords: ISO 27001, SOC 2, NIS2 · DORA
Live recon
Within hours of kickoff, REVENGE maps every subdomain, endpoint, cloud account and LLM integration you own, including the ones you forgot. Then our operators go to work.
## We see what attackers see, first.

Within hours of kickoff, REVENGE maps every subdomain, endpoint, cloud account and LLM integration you own, including the ones you forgot. Then our operators go to work.

- **72h** to your first validated critical finding
- **15min** incident response SLA, 24/7/365
- **0** unverified findings in your report
- **100%** of findings ship with a code-level fix
The REVENGE Grid
The REVENGE Grid connects to every layer you run (code, pipelines, cloud, identity and AI agents) and correlates their signals into one picture of how you'd actually get breached.
## One brain at the heart of your defenses.

The REVENGE Grid connects to every layer you run (code, pipelines, cloud, identity and AI agents) and correlates their signals into one picture of how you'd actually get breached.

- Correlated attack paths: Findings from every layer are linked into attack paths, so you fix the one choke point instead of a thousand tickets.
- Agent-aware by design: It tracks which tools, data and permissions your AI agents can reach, before an injected prompt uses them.
- Operators in the loop: Automation finds the signal. Humans with offensive experience decide what's real and act on it.
Readable by humans and machines
Your board gets the picture and your AI assistants get clean markdown, each in the format it reads best.
Validated critical findings land in your backlog within three days of kickoff, instead of in a PDF six weeks later.
Incident response operators engage within 15 minutes, day or night, customer or not.
If we can't exploit it, it doesn't go in your report, so your engineers only spend time on real issues.
Every page on this site has a markdown twin and a machine-readable index for LLMs: /index.md /llms.txt /llms-full.txt
## Built for humans. Parsed by agents.

Your board gets the picture and your AI assistants get clean markdown, each in the format it reads best.

### First critical, fast

**72h**: Validated critical findings land in your backlog within three days of kickoff, instead of in a PDF six weeks later.

### Operators on the line

**15′**: Incident response operators engage within 15 minutes, day or night, customer or not.

### False positives

**0**: If we can't exploit it, it doesn't go in your report, so your engineers only spend time on real issues.
Compare
Here's how REVENGE stacks up against the usual options.
| REVENGE | Traditional pentest firm | Automated scanners | In-house team only | |
|---|---|---|---|---|
| Human-led exploitation of business logic | Yes | Yes | No | Partial |
| AI & LLM red teaming | Yes | No | No | Partial |
| Every finding validated with a working exploit | Yes | Partial | No | Partial |
| Fix delivered as code (pull request) | Yes | No | Partial | Yes |
| Continuous testing, not once a year | Yes | No | Yes | Partial |
| 15-minute incident response, 24/7 | Yes | No | No | No |
| Audit-ready compliance evidence | Yes | Partial | No | Partial |
| Time to first critical finding | 72 hours | 3 to 6 weeks | Minutes (mostly noise) | Depends on headcount |
## Not another pentest PDF.

Here's how REVENGE stacks up against the usual options.

| | REVENGE | Traditional pentest firm | Automated scanners | In-house team only |
|---|---|---|---|---|
| Human-led exploitation of business logic | ✅ | ✅ | ❌ | ◐ |
| AI & LLM red teaming | ✅ | ❌ | ❌ | ◐ |
| Every finding validated with a working exploit | ✅ | ◐ | ❌ | ◐ |
| Fix delivered as code (pull request) | ✅ | ❌ | ◐ | ✅ |
| Continuous testing, not once a year | ✅ | ❌ | ✅ | ◐ |
| 15-minute incident response, 24/7 | ✅ | ❌ | ❌ | ❌ |
| Audit-ready compliance evidence | ✅ | ◐ | ❌ | ◐ |
| Time to first critical finding | 72 hours | 3 to 6 weeks | Minutes (mostly noise) | Depends on headcount |

Legend: ✅ Included · ◐ Partial / extra cost · ❌ Not available
Integrations
REVENGE sends findings and fixes straight into your IDEs, repositories, CI/CD pipelines, ticketing, clouds and AI coding assistants, so your engineers stay in their own tools.
View all integrations


## Security that plugs into how you already ship.

REVENGE sends findings and fixes straight into your IDEs, repositories, CI/CD pipelines, ticketing, clouds and AI coding assistants, so your engineers stay in their own tools.

Claude, GitHub, GitLab, Bitbucket, Jenkins, GitHub Actions, Cursor, Docker, Kubernetes, Terraform, Google Cloud, Cloudflare, Vercel, Anthropic, Jira, Kali Linux, Linear, PagerDuty, Datadog, Splunk, JetBrains, Okta, Auth0, Vault, Sentry, Grafana, Elastic, Argo, Python, Go, Node.js, Rust, Android, Linux, Helm
The operators
Our red teamers, exploit developers, AI researchers and incident responders have spent their careers breaking into hard targets.
## Ex-attackers. Now on your side.

Our red teamers, exploit developers, AI researchers and incident responders have spent their careers breaking into hard targets.

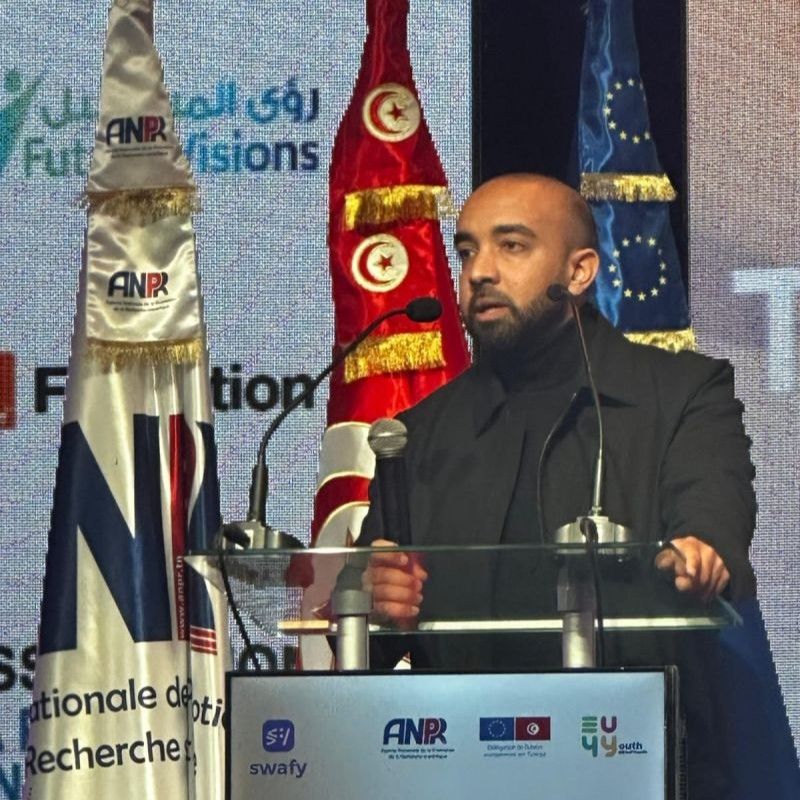
- Riadh Jouini, Co-founder & CEO: Leads REVENGE's strategy, partnerships and client relationships, and keeps every engagement focused on fixes your team can ship. LinkedIn: https://www.linkedin.com/in/riadh-jouini
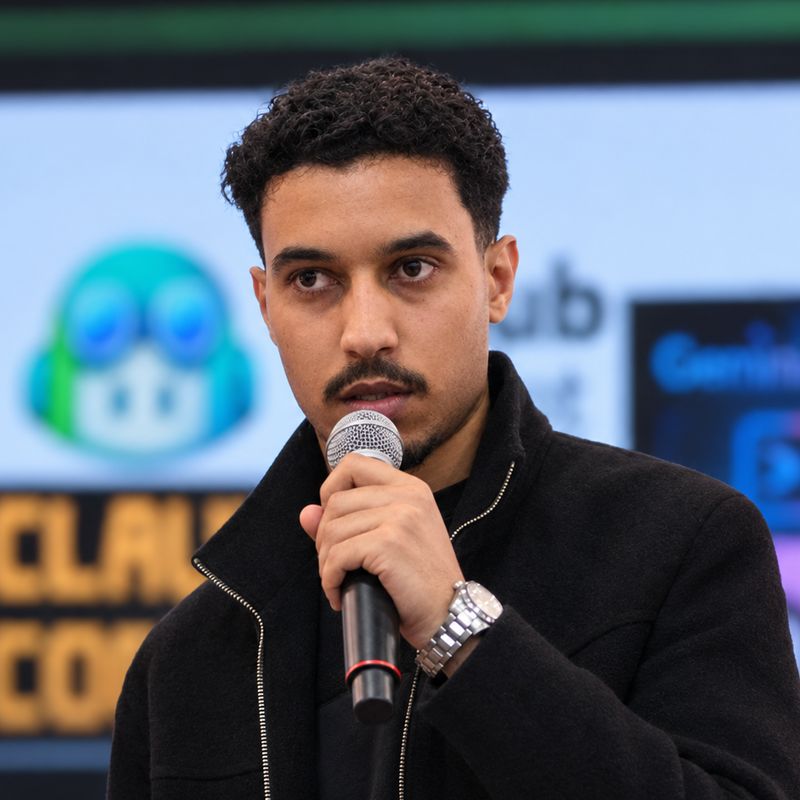
- Jihed Kdiss, Co-founder & CTO: Leads REVENGE's technology and offensive engineering, from the REVENGE Grid to how operators run each engagement. LinkedIn: https://www.linkedin.com/in/jihedkdiss
FAQ
Still have questions? Our operators reply to every message.
REVENGE is an offensive security company. We run penetration tests, red team operations and AI/LLM red teaming against your web apps, APIs, cloud and AI systems, validate every finding with a working exploit, deliver fixes as code, and provide 24/7 incident response with a 15-minute SLA.
Traditional firms deliver a PDF weeks after testing ends. REVENGE delivers validated critical findings within 72 hours, ships the fix as a pull request, retests automatically, and keeps attacking continuously instead of once a year.
Yes. We red team chatbots, RAG pipelines and autonomous agents for prompt injection, jailbreaks, tool and plugin abuse, sensitive data leakage, insecure output handling and model theft, aligned with the OWASP Top 10 for LLM Applications and the EU AI Act.
Yes. Use the 'Under attack?' button at the top of every page or email contact@revengeaisecurity.com. Operators engage within 15 minutes, 24/7/365, whether or not you're a customer.
Yes. Our testing and reports are built to produce audit-ready evidence, and our compliance team maps findings and remediations directly to the controls your auditor will check.
Every engagement follows agreed rules of engagement, written authorization and safe-exploitation practices. Destructive tests run only in environments you approve, and you can halt testing at any time.
## FAQ

### What does REVENGE do?

REVENGE is an offensive security company. We run penetration tests, red team operations and AI/LLM red teaming against your web apps, APIs, cloud and AI systems, validate every finding with a working exploit, deliver fixes as code, and provide 24/7 incident response with a 15-minute SLA.

### How is REVENGE different from a traditional pentest firm?

Traditional firms deliver a PDF weeks after testing ends. REVENGE delivers validated critical findings within 72 hours, ships the fix as a pull request, retests automatically, and keeps attacking continuously instead of once a year.

### Do you test AI and LLM applications?

Yes. We red team chatbots, RAG pipelines and autonomous agents for prompt injection, jailbreaks, tool and plugin abuse, sensitive data leakage, insecure output handling and model theft, aligned with the OWASP Top 10 for LLM Applications and the EU AI Act.

### We're under attack right now. Can you help even if we're not a customer?

Yes. Use the 'Under attack?' button at the top of every page or email contact@revengeaisecurity.com. Operators engage within 15 minutes, 24/7/365, whether or not you're a customer.

### Will you help us with ISO 27001, SOC 2, PCI DSS, NIS2 or DORA?

Yes. Our testing and reports are built to produce audit-ready evidence, and our compliance team maps findings and remediations directly to the controls your auditor will check.

### Is testing safe for production?

Every engagement follows agreed rules of engagement, written authorization and safe-exploitation practices. Destructive tests run only in environments you approve, and you can halt testing at any time.